

HIBAPRESS
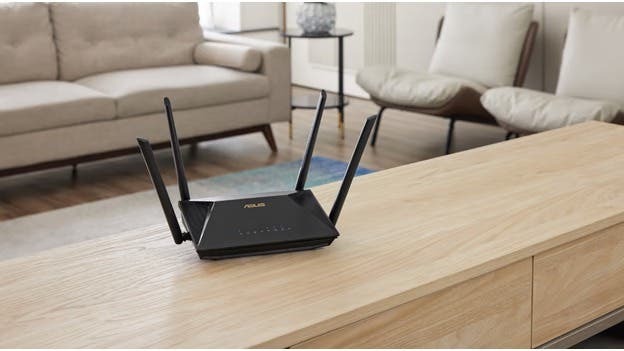
The Directorate General for the Security of Information Systems, under the National Defense Administration, has warned of a dangerous cyber vulnerability in three models of “ASUS” router devices: DSL-AC51, DSL-N16, and DSL-AC750 with version "1.1.2.3_1010".
The vulnerability, known by the code CVE-2025-59367, is classified as "critical" due to the potential for direct breaches of network security. The Directorate explained that the manufacturer has released an update to address the flaw, but devices that have not yet updated remain exposed to a risk that allows hackers to bypass protection mechanisms, control device settings, intercept data, or execute malicious operations that threaten home and professional networks. The Directorate called on all users of these devices to quickly update them by referring to the ASUS security bulletin issued on November 13, 2025, emphasizing the importance of taking preventive measures to enhance data protection. It also made available the support channels of the MaCERT center to provide the necessary technical guidance.